hMailServer Alert Test
Testing my own hMailServer failed-login detection: eleven failed logins from a Thunderbird client raise Wazuh rules 100321 and 100322, open a LabWatch incident, and get triaged step by step.
A portfolio dedicated to my cybersecurity journey.
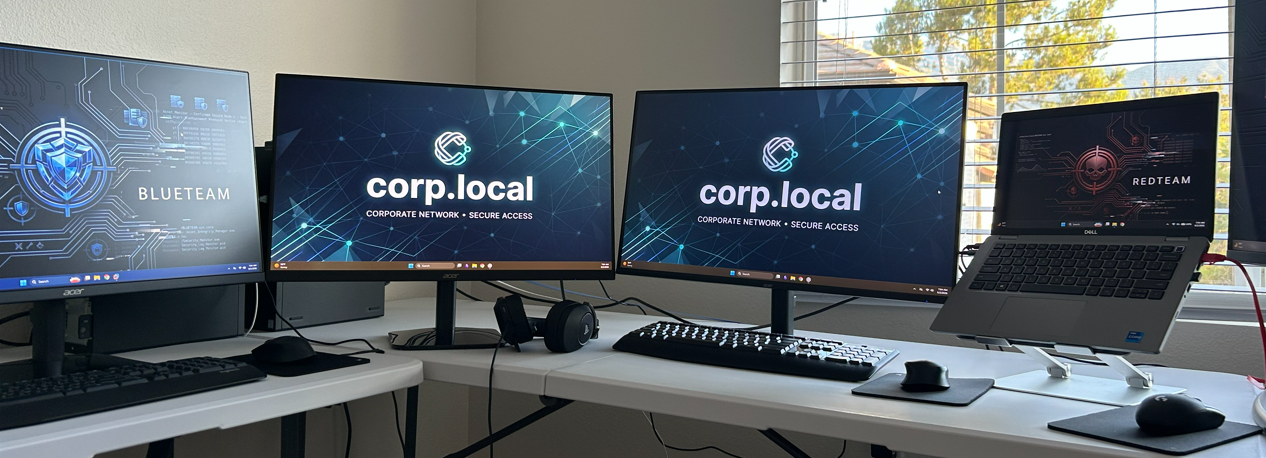
I built an Active Directory lab with two Windows 11 endpoints, a shared application server, Wazuh detection, Elasticsearch/Kibana analysis, a Kali workstation, and a Suricata/Zeek network sensor. SRV01 combines deliberately vulnerable web practice with protected document and incident-management services. I use the lab to investigate alerts, test detections, troubleshoot failures, and document recovery.
| VM | Role | Platform | Core technologies |
|---|---|---|---|
| DC01 | Identity and directory | Windows Server 2022 | AD DS · DNS · Kerberos · lab certificate authority |
| SRV01 | Applications and practice range | Windows Server 2022 | IIS/PHP · MySQL · hMailServer · Corp Documents · LabWatch · DVWA · BountyAPI |
| WS01 / WS02 | Instrumented endpoints | Windows 11 | Sysmon · Wazuh · Velociraptor |
| SIEM01 | Detection and DFIR | Ubuntu 26.04 | Wazuh · Velociraptor · Elastic alert forwarder |
| SIEM02 | Analytics and decision layer | Ubuntu 26.04 | Elasticsearch · Kibana · Wazuh and network analysis |
| KALI | Adversary emulation | Kali Linux | Nmap · Impacket · NetExec · BloodHound |
| NDR01 | Passive network sensor | Ubuntu 26.04 | Suricata · Zeek · mirrored switch traffic |
Testing my own hMailServer failed-login detection: eleven failed logins from a Thunderbird client raise Wazuh rules 100321 and 100322, open a LabWatch incident, and get triaged step by step.
The first round of a homelab exercise: Claude Code injects a real fault and files a ticket, and I work it blind as a live incident. One workstation cannot reach an internal web app while every other host and port is fine. The cause is a single outbound firewall rule, found by listing rules on what I knew instead of a guessed name and pinned to its port and address by a shared InstanceId.
A September snapshot of my SOC homelab, from physical hosts and Active Directory to Wazuh, Velociraptor, the former Splunk and C2 roles, and LabWatch incident response.
AS-REP roasting and AES Kerberoasting captured from KALI, traced through DC01 events, detected in Wazuh, inspected in Wireshark, and tested with offline cracking.
One remote-access tool on a machine is normal; every managed service provider has one. The useful question is whether a second one showed up and whether the first one put it there. Four Wazuh rules built and fired against a live workstation, and the vendor-list gap that made the rule miss a real campaign.
The service came up on the first try, then I deleted it and rebuilt it because I could not have said what half of it was doing. Two version-pinned traps, including a config generator offering to write private keys onto a network share.